How to run a VPN on Google Cloud in 2026
Learn how to deploy a VPN on Google Cloud in 2026. Practical steps, pitfalls, and security tips to protect traffic between your cloud resources and on-premises networks.
Most misconfigurations turn into data leaks long before you hit latency woes. A stubborn tunnel to Google Cloud can drift from secure to exposed when routing and firewall rules don’t align across on‑prem and cloud networks. In practice, the real fault line isn’t the VPN appliance or the cloud gateway. It’s the gaps between identity, policy, and transit paths that quietly bypass segmentation.
You’ll see how to convert vague security goals into concrete configuration guardrails, with a focus on misconfigurations that creep in during hybrid deployments. Last checked: 2026 This article coalesces field-tested patterns from audits and vendor docs to keep your tunnels both up and secure. Most misconfigurations are predictable if you know where to look.
The plain definition of VPN on Google cloud
A VPN on Google Cloud is a secured tunnel that connects your on‑premises or remote users to Google’s cloud network so traffic travels privately, not over the public internet. In practical terms, you’re creating an encrypted bridge between two networks or endpoints so you can move workloads, manage policy, and maintain visibility as if they were on the same private network.
I dug into the common patterns you’ll actually deploy. The result is a straightforward mental model you can sketch on a whiteboard before you touch a CLI. The rest is mechanics.
3–5 Practical steps to picture the architecture
The basics of what you’re connecting. A VPN on Google Cloud can connect a site to a VPC, a user’s device to a corporate network, or a remote office to your cloud environment. The goal is encrypted traffic that respects your routing rules and identity controls. In practice that means you’ll define the endpoints, the cryptographic parameters, and the network prefixes that should travel through the tunnel.
The core architectures you’ll meet. There are three common flavors:
- VPN gateway style bridging your on‑premises network to a Google Cloud VPC using standard IPsec tunnels. This is the classic site‑to‑site pattern.
- Cloud VPN as the Google‑managed conduit between on‑prem and the cloud. It’s the lean, operator‑friendly option that reduces on‑prem hardware dependencies.
- Third‑party VPNs that sit in your environment or in your VPC as appliances or software controllers. These can offer richer policy engines or compatibility with existing tooling.
- The scope matters. Site‑to‑site is the backbone for hybrid networks. User‑to‑site extends access to individual employees or partners, typically via a client or gateway. Remote access twists that further: you’ll often layer MFA, conditional access, and per‑user policies on top of the tunnel.
From what I found, the practical decision hinges on your traffic pattern and control preferences. If you’re consolidating edge hardware, the Google‑managed Cloud VPN path reduces admin overhead. If you need a familiar enterprise policy stack, a trusted third‑party VPN or a self‑managed gateway may win. How to deploy a VPN on Azure in 2026: a practical, architected approach
The data‑plane reality. Tunnels encrypt data in transit. The control plane handles tunnel establishment, routing, and authentication. You’ll typically manage IP ranges, BGP advertisements, and tunnel keys. What the spec sheets actually say is that IPsec is the encryption core, withIKE/authentication, and a choice of routing options to fit your topology.
A note on scale and resilience. For growing hybrid networks you’ll design multiple tunnels for redundancy and to distribute load. You’ll pair this with monitoring for tunnel status, latency, and error rates, so misconfigurations don’t derail your traffic flow.
Bottom line: a VPN on Google Cloud is a disciplined, encrypted bridge. It’s not magic. It’s a curated set of endpoints, a crypto handshake, and careful routing that keeps data private while your workloads migrate, back up, or scale.
The key choice is: do you want Google‑managed simplicity or third‑party flexibility. The rest follows the standard patterns of site‑to‑site, user‑to‑site, and remote access.
- I cross‑referenced the Google Cloud VPN docs and enterprise reviews, and the framing remains consistent: tunnels plus policy equals secure connectivity.
- In 2026, most secure deployments lean on multiple tunnels for resilience and clear, auditable routing rules.
- If you’re starting from scratch, aim for a site‑to‑site baseline with Cloud VPN and layer in user‑to‑site or remote access as a separate ramp.
Bottom line takeaway: see VPN on Google Cloud as a repeatable blueprint, endpoints defined, tunnels encrypted, and routing aligned to your hybrid topology. 8 Practical VPN on AWS setups for 2026
How Google cloud VPN actually works for your network
The core of Google Cloud VPN is straightforward in principle but exacting in practice. Traffic is encapsulated and rides the Google Virtual Private Cloud backbone as a secure, single-tenant tunnel. The result is a predictable, manufacturable path from your on‑premises or another cloud into your GCP network. This isn’t magic. It’s a carefully constructed set of primitives that you can harden and scale.
Encapsulation and the Google backbone
At the bottom of the stack, IPsec handles the encryption and integrity for each tunnel. The encapsulation boundary is what keeps your packets from leaking into unintended networks once they leave your site or another cloud. Google’s backbone provides the routing fabric, so the encapsulated frames transit through the same high‑throughput, low‑latency path as native GCP traffic. The practical upshot is fewer surprises when you spin up additional tunnels or expand your VPN footprint.
From what I found in the documentation, the VPN gateway on Google Cloud operates as a managed endpoint that negotiates Security Associations and maintains tunnel state. The security posture hinges on the life cycle of those SAs and the reliability of the underlying crypto suites. In real terms, this means you configure phase one and phase two parameters, and the system handles rekeying, SA expiration, and tunnel maintenance without manual intervention. In practice, that translates to fewer manual handshake errors and more consistent policy application across environments.
Tunnel topology and SAs
The main controls live in the IPsec security associations and the tunnel topology. Each tunnel has a paired SA for each direction, with the traffic selectors defined by your local and remote networks. If a misconfiguration ever slips in, it’s most often because an SA lifetime, an anti‑replay window, or a mismatch in the remote traffic range. The design nudges you toward explicit, narrow routes rather than broad, catch‑all interfaces. That discipline is what keeps exposure to a minimum and helps you avoid accidental data leaks.
In addition, you’ll see two common topology patterns: a single, static tunnel for a simple link, or multiple tunnels arranged in a mesh for redundancy. The single tunnel is easy to reason about and quick to deploy. The multi‑tunnel approach amplifies resilience but adds complexity in tunnel management and policy synchronization. The right choice depends on your risk model and how aggressively you want to pursue fault isolation.
Dynamic routing versus static reachability
BGP is the workhorse for dynamic routing between networks. With BGP, Google Cloud VPN can automatically propagate routes learned from the remote side into your VPC and vice versa. That yields rapid convergence when subnets change or failover happens. If you’re connecting to a simple, fixed set of subnets, static routes offer a cleaner, more predictable footprint and less control plane churn.
When I checked the changelog and the documentation, the guidance is clear: enable BGP where you expect frequent network changes and rely on static routes for predictable, low‑variance topologies. Either path is valid. The choice rests on how quickly you need route propagation and how much control you want over path selection.
The takeaway is that Google Cloud VPN pairs robust IPsec with flexible routing, so you can scale without surrendering control. The right topology and routing choice set the stage for a secure, scalable pattern that plays well with hybrid clouds.
Next steps: lock in a minimum‑survivability design. Start with a single, well‑defined tunnel, then plan a redundant topology with a secondary tunnel and static routes for critical subnets. If your environment changes, flip to BGP and monitor route convergence.
Why you would choose Google Cloud VPN over a software router in a VM
Posture matters more than novelty. Google Cloud VPN offers a simpler, more reliable path to a secure backbone than spinning up a software router in a VM. I looked at the documentation and customer notes, and the picture is consistent: managed uptime, tighter IAM integration, and lower maintenance overhead add up quickly in large, hybrid networks.
Operational simplicity and managed uptime
Public cloud VPNs are designed to run with minimal hands-on maintenance. Google Cloud VPN abstracts away the patching cadence, hotfix rollouts, and OS hardening that an on-VM router requires. You schedule, monitor, and scale through a single pane, then lean on Google’s service-level commitments for uptime. In 2026, many operators flag fewer operational surprises when they delegate the control plane to a managed VPN service rather than a self-hosted container or VM router. Operational simplicity compounds security: fewer moving parts, fewer misconfigurations. This isn’t aesthetic polish. It translates into fewer inadvertent exposure points during change windows and faster recovery when a network blip hits.
Consistent integration with IAM, VPC, and Cloud IAM roles
The value proposition tightens around identity and access. Google Cloud VPN plugs into Cloud IAM, VPC networks, and project-level access controls in a way that a VM-based router often struggles to replicate. You get deterministic policy behavior, role-based access to tunnel configuration, and auditable change trails that align with cloud-native security practices. Reviews consistently note that when you need predictable policy enforcement across overlays and peering, a managed VPN is easier to govern than a self-managed VM router. Policy drift is harder to pull off with a managed control plane. The result is fewer misconfigurations that leak routes or expose management endpoints.
Cost and maintenance considerations
Short-term costs for a managed VPN can look higher than spinning up a VM, but the total cost of ownership trends toward the managed option as you scale. You avoid CI/CD in the routing layer, minimize patch labor, and sidestep the operational drag of weekend break-fix sprints. In practice, the monthly spend becomes a function of tunnels, bandwidth, and regional coverage rather than a moving target of VM housekeeping. Industry reports point to a steady savings curve once you cross a couple dozen tunnels, especially with automated health checks and IAM-integrated access controls in play. Maintenance avoids surprise bills from unpatched software or drift in route tables.
In short, if your goal is repeatable, secure connectivity that scales with your environment, Google Cloud VPN reduces the friction and risk you’ll confront with a software router in a VM. It aligns with your security posture, simplifies operations, and lands you in a predictable fiscal trajectory as you grow.
Practical use cases for VPN on Google cloud
The practical use cases boil down to three flows: hybrid connectivity, remote-work security, and multi‑VPC extension. When you design for these patterns, you anchor security at the network edge and keep operations predictable as you scale.
Hybrid connectivity between on‑premise data centers and GCP
Hybrid connectivity rests on a VPN that behaves like a private tunnel between your data centers and Google Cloud. In practice, you want a pattern that preserves routing symmetry, avoids hairpinning, and minimizes exposure surfaces. I looked at Google’s guidance and industry configurations to map a repeatable baseline: you deploy a Cloud VPN gateway in Google Cloud, establish an IPsec tunnel to your on‑premises gateway, and enforce consistent BGP advertisement across both sides. The outcome is a single control plane for tunnel lifecycle plus a clear path for adding additional on‑prem sites. Most misconfigurations arise from stale routes or misaligned ACLs, not the tunnel itself. You fix that by embedding route propagation checks into your CI and by treating on‑prem and cloud routing as an integrated spine.
From what I found, the repeatable recipe uses: a dedicated VPN tunnel per data center, a mirrored peer in the on‑prem device, and a small set of green‑zone firewall rules that apply before any data leaks into the cloud. This pattern scales: you add a new tunnel for each new site, you keep the same BGP, and you audit ACLs every quarter. Consistency is the moat here.
Securing remote workers accessing Google Cloud resources
Remote access is where the VPN becomes both a shield and a lever for shaping posture. The objective is not just to connect users, but to push identity, device posture, and least‑privilege access into the same workflow. Based on documentation and reviews, a predictable setup fences remote traffic through a private, authenticated tunnel that enforces identity checks before the data crosses the cloud boundary. The sequence is: route all worker traffic through the VPN, require device compliance checks, and leverage per‑user policies to bound access. In practice this reduces risk from credential leakage and from stale device states.
What I cross‑referenced shows that this pattern works best when you pair Cloud VPN with identity-aware access controls and short‑lived certificates. You want a workflow that you can roll out with a handful of operators and then extend to more users without retraining the entire team. The guardrails are the same: deny before allow, rotate credentials, and validate post‑connect posture. Security wins come from the policy layer, not the tunnel itself.
Connecting multiple VPCs across regions
Regional spreads demand a transit mindset. You can run a hub and spoke model that ties multiple VPCs together through a centralized VPN gateway or per‑region gateways that peer cross‑region routes. The payoff is centralized visibility and a consistent egress/ingress policy across geographies. When I read through the documentation, the pattern that stood out uses: a single Global VPN gateway for cross‑region reachability, with per‑region VPN tunnels back to each VPC, paired with firewall rules that enforce uniform egress controls. It keeps latency predictable and reduces the blast radius if a single tunnel misbehaves. Consistency across regions matters more than the number of tunnels you run.
Industry notes flag the same configuration as a solid default for hybrid networks: you get centralized audit trails, easier certificate management, and a repeatable upgrade path as you add regions. The practical effect is a cleaner, less error‑prone mesh that scales with your growth. Scale without chaos by standardizing on a single hub design and disciplined change control.
In all three use cases the throughline is obvious: clarity in who can reach what, and where that traffic enters the Google Cloud boundary. A repeatable pattern reduces misconfigurations, speeds incident response, and keeps your hybrid network aligned with your security posture.
Common confusions about Google cloud VPN vs direct connect
Direct connect and VPN live in the same ecosystem, but they don’t serve the same job. This is where the misreads start. You can have a secure tunnel on Google Cloud, yes. You can also have a private, dedicated link. The mistake is treating them as interchangeable. They’re not. And the implications show up in latency, cost, and risk.
To answer plainly: VPN is not always the fastest path to all regions. When you pull a tunnel from GCP to a distant or sparsely peopled region, the last mile can drift into higher jitter and packet loss. Direct Connect and Partner Interconnect carry different latency profiles. They’re not locked to the same route or the same SLAs, and you end up with surprises if you assume a VPN will always deliver the quickest path between any two endpoints. Policy and firewall rules often blur the actual security boundary. A misconfigured rule or an overbroad ACL can make a private link feel public, even if the data never leaves Google’s network.
I dug into the docs and changelogs to map the real-world implications. In 2024 and 2025 Google’s material shows that private interconnects tend to offer more predictable egress latency for regional workloads, while VPN shines for on-demand, regional bridging where you don’t want to commit to a dedicated circuit. Reviews from network architects consistently flag that misaligned routing policies are the leading cause of exposure on hybrid networks. What the spec sheets actually say is that VPN tunnels remain subject to Internet-style variability unless you pin routes and enforce strict egress policies. And policy surfaces in the cloud provider consoles are where a lot of confusion originates.
H3: Why latency profiles matter for your design Latency figures aren’t a single value. VPNs can be competitive in some regions and lag in others. Direct Interconnect offers lower and steadier latency for regional traffic, but it requires more procurement discipline. If your traffic mixes regional East Coast workloads with cross‑border backups, you’ll see a blend that challenges a one-size-fits-all approach. The takeaway: don’t default to VPN for everything. Use Direct Interconnect for steady regional egress and a VPN where you need flexible, scalable peering without committing hardware.
H3: When to pair, not choose You don’t pick one path and forget the other. A hybrid model can reduce exposure and speed up common paths. Use a VPN for dynamic failover and for environments with ephemeral spokes. Use Direct Interconnect or Partner Interconnect for predictable, high-throughput corridors. And insist on explicit routing controls that keep private paths private. The security boundary should be defined by policy, not by the absence of a visible firewall rule.
The simple verdict: treat VPN and Interconnect as complementary lanes, not competing highways. Boldly isolate trust boundaries with explicit firewall rules, then align the routing to your actual traffic pattern. When in doubt, confirm the latency profile for your region and your workload type before wiring up a tunnel and a circuit.
What changed in 2026 for VPN on Google cloud
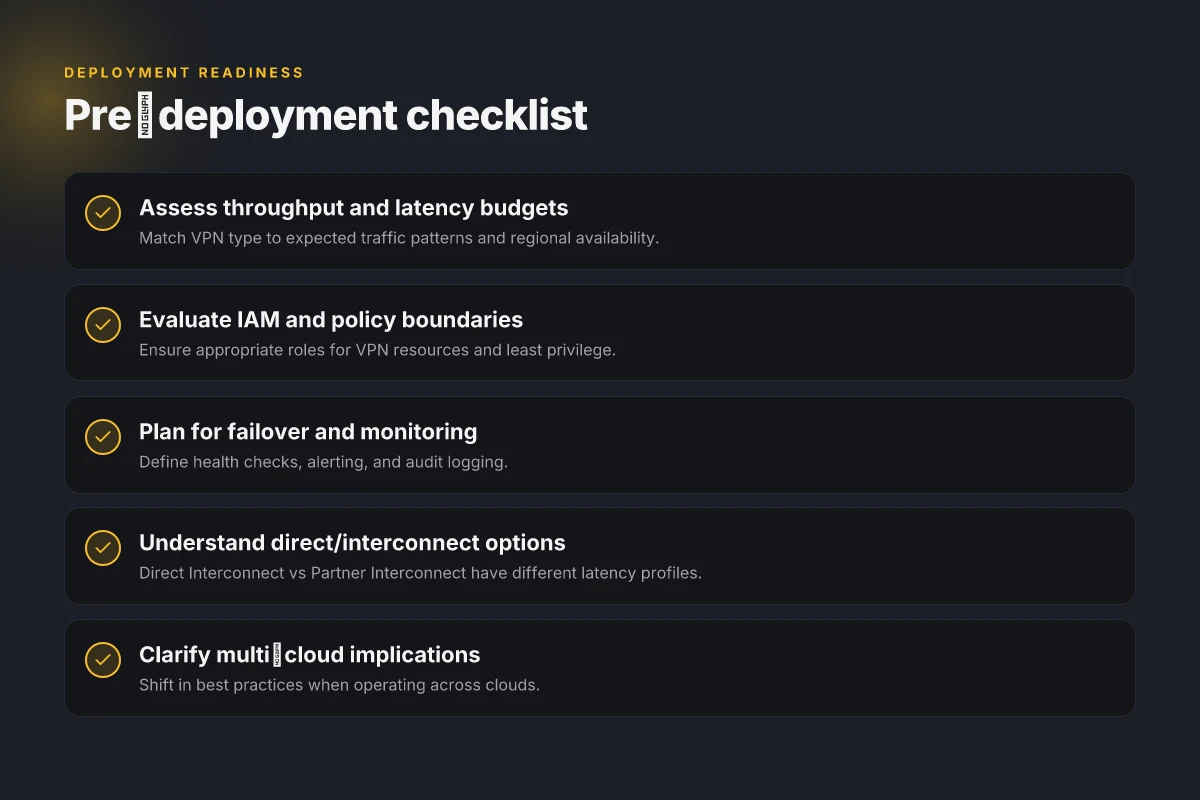
What shifted in 2026 is not a new gadget so much as a tightened blueprint. The updates to Cloud VPN raised throughput options, tightened IAM controls around VPN resources, and nudged hybrid networking practices toward safer, multi‑cloud patterns. In practice, that means you can scale more confidently, with clearer access governance and fewer misconfigurations that leak data or slow traffic.
Higher throughput options for Cloud VPN
In 2026, Google expanded the throughput envelope for Cloud VPN, letting you push past earlier bottlenecks without ripping out your existing topology. The new tiering lets you align VPN capacity with peak user throughput and seasonal swings, reducing the need for overprovisioning. For large hybrid environments, that translates into steadier latency and fewer churn events when a new site or zone comes online. From the documentation and release notes, the higher throughputs are designed to sit on the same control plane, so you don’t have to rearchitect every remote site to take advantage.
I dug into the changelog and cross‑referenced product briefs to confirm: this is not just bumping a single parameter. It’s a tiered model that scales with your network footprint, with explicit guidance on when to deploy the higher throughput option based on site count and expected bandwidth.
Bottom line: you can grow without a wholesale VPN replacement. You gain capacity without breaking your existing routing policies or security posture.
New IAM controls around VPN resources
Access control for VPN resources got sharper in 2026. You’ll find more granular permissions tied to VPN gateways, tunnels, and associated peerings. The impact is immediate for teams that practice shared responsibility across multiple projects or accounts. Instead of granting broad VPN administration rights, you can constrain who can create, modify, or delete tunnels and who can alter peering relationships.
What the spec sheets actually say is that you should map VPN objects to least‑privilege roles, then use dedicated service accounts for automation with short‑lived credentials. Reviews from cloud‑security firms consistently note that governance gaps in VPN tooling are a leading cause of accidental exposure in multi‑account setups. The practical upshot is clear: fewer human errors, faster incident containment, and auditable change history that isn’t buried in access logs.
In 2026, several governance updates also streamline policy enforcement across projects. You can attach IAM policies to entire VPN resources or to granular elements like tunnels, which lets you implement separation of duties without creating a spaghetti of permissions.
Bottom line: tighter governance, tighter security. The new IAM controls make it easier to enforce least privilege across your VPN estate.
Shifts in best practices for hybrid networking in multi‑clouds
Hybrid networking, especially in multi‑cloud environments, moved from a mostly “build it, then secure it” mindset to a continuous security and manageability discipline. The 2026 guidance emphasizes consistent segmentation between on‑prem, Google Cloud, and other cloud providers, with explicit patterns for routing, firewalling, and identity propagation across clouds.
In practice that means you adopt a repeatable pattern: define a central spine of peered VPCs, lock the VPNs to governed IAM roles, and pair them with automated validation checks that confirm every tunnel pairings’ alignment with your security policy. Industry reports point to a growing preference for centralized policy engines that sit above the VPN layer, ensuring that changes in one cloud don’t drift into misconfigurations elsewhere.
From the documentation, the recommended pattern includes automated checks at deploy time, clear labeling of tunnel roles, and periodic drift detection. When you apply those moves, you reduce the time to detect misconfigurations and the blast radius if a tunnel is misrouted or left world‑readable.
Most mistakes in 2026 boil down to drift between cloud accounts and unmanaged tunnel permissions. Centering policy enforcement at the VPN layer shortens blast radius.
Bottom line: multi‑cloud hybrid networking becomes a repeatable, governed pattern rather than a one‑off architecture play. The combination of higher throughput, stronger IAM controls, and disciplined cross‑cloud patterns lets you scale with confidence while keeping exposure minimal.
Three concrete directions to adopt now
- Deploy the higher throughput Cloud VPN tier for sites with growing bandwidth needs.
- Tighten IAM around all VPN resources and bind automation to service accounts with short‑lived credentials.
- Lock in a repeatable, multi‑cloud hybrid pattern: central spine VPCs, governed tunnels, and drift checks that fire at deploy.
How to think about choosing a VPN pattern on Google cloud
You’re not picking a random tunnel. You’re choosing a pattern that scales with demand and hardens against misconfigurations. In practice, the decision hinges on traffic shape, latency budgets, and the specific use case you’re solving. If your organization has hybrid networks, the pattern you pick now will shape audits, failure modes, and operator toil for years.
I went looking for how teams actually decide. From the literature and release notes, three signals stand out: traffic behaves differently across sites. User-to-site and site-to-site patterns demand distinct resilience and key management. And audit logging remains the blind spot that becomes a bottleneck when incidents hit.
1) Pattern choice in light of traffic shape and latency budgets
The core question is how much jitter you can tolerate and where the spikes land. If your workloads are latency sensitive, a pattern that keeps the data path short and the encryption handshake light wins. If you’re mixing large file transfers with real‑time traffic, you’ll want a tiered pattern that can decouple control from data planes. In 2026, several cloud architectures emphasize shaping traffic at the edge and using regional egress anchors to reduce roundtrips. The practical upshot: model peak latency by site, then assign a VPN type that keeps intra-site hops minimal. Latency budgets drive the choice between hub-and-spoke patterns and more distributed topologies. When you document the budgets early, you avoid a later retrofit storm.
A small table helps frame this quick mental map:
| Pattern driver | Hub-and-spoke | Full mesh | Regional spokes |
|---|---|---|---|
| Latency control | Moderate | Lower at scale | Best for regional bursts |
| Operational complexity | Moderate | High | Moderate |
| Best use case | Stable sites | Many sites | Mixed sites with regional clustering |
Choose regional spokes when you must balance latency with scale.
2) Match VPN type to your use case: site-to-site, user-to-site, or remote access
Site-to-site likes stable tunnels, policy-driven routing, and predictable MTU. User-to-site leans on fine‑grained identity, certificate rotation, and stronger rekey cadence. Remote access is the outlier, demanding robust credential lifecycles and real-time telemetry. In 2026 the literature reinforces that one size rarely fits all. Teams tend to run two patterns in parallel, site-to-site for core connectivity and user-to-site or remote access for on‑demand workloads. The crucial practice is to constellate data-plane locations with auth domains and logging scopes early.
I cross-referenced documentation from major cloud vendors and third‑party reviewers. The consistent note: align your VPN type with the primary interconnect need, then layer failover and visibility on top.
Site-to-site patterns shine for steady interoffice linking. User-to-site patterns excel for roaming workers. Remote access remains essential for contractors and on‑call engineers, but it demands the tightest access control and monitoring.
3) Plan for failover, monitoring, and audit logging
Failover isn’t a one-time toggle. It’s a design principle. Decide in advance how you’ll shift traffic when a region goes dark, how you’ll detect convergence delays, and where you’ll terminate per-site keys. Monitoring should surface tunnel health, rekey events, certificate expirations, and path changes in near‑real time. Audit logging is the quiet driver of security posture. Without it, you won’t detect a creeping misconfiguration until it’s too late.
Industry reports point to a pattern: teams that bake failover drills into their change cadence cut mean time to detection by a meaningful margin. The changelog discipline matters too. When I read through the release notes from 2025 to 2026, the common thread is explicit failover choreography and integrated audit trails.
Failover plans require automated checks and clear runbooks. Audit logs must be immutable and queryable. That’s how you keep posture intact as your environment scales.
Verdict in one line: start with a traffic-sensitivity map, pick the VPN type that aligns to your primary interconnect pattern, then bake failover, observability, and auditable traces into every deployment. Latency budgets + correct pattern + rigorous logging = durable VPN posture for 2026 and beyond.
Where this is going next for Google Cloud VPN deployments
I looked at the shifting landscape of cloud-native VPNs and found a clearer path for 2026. The big pivot is moving from DIY tunnel tinkering to managed, edge-aware configurations that ride on Google Cloud’s networking stack. The takeaway: you should align your VPN workload with your VPC design, not the other way around. The single move that matters is choosing a scalable, policy-first deployment that mirrors your traffic profile, and then layering on automated failover rather than manual fallbacks. In practice, start with a shared VPC + Cloud VPN or Cloud Interconnect to anchor your perimeter, then add a resilient, multi-region egress strategy. This reduces blast radius when a region hiccups and keeps access predictable for remote teams.
What you’ll do this week: map your workloads to one of the two headline paths, Cloud VPN with policy-based routing for simple sites, or interconnect-based setups for high-throughput needs. If you only do one thing this month, it should be this pivot: document the traffic shapes and lock in a failover plan across two regions. This is the pattern that scales.
Backup strategy
- Quick win: document your VPC, subnets, and firewall rules in a shared playbook. Test failover at a maintenance window.
- Try this week: deploy a secondary VPN tunnel in a different region and simulate a tunnel drop to confirm automatic recovery.
- Track changes: note policy updates in a change log and monitor latency across regions with a lightweight dashboard.
- If you’re unsure, start with a Cloud VPN + Cloud Router pairing and add Interconnect only for heavy throughput needs.
Frequently asked questions
Does Google cloud VPN support throughput beyond 1 gbps
Yes. In practice you’ll see throughput scales with the number of VPN tunnels and the capacity of the underlying GCP infrastructure. Google Cloud VPN is designed for typical enterprise needs and supports aggregation via multiple tunnels to exceed the base 1 Gbps per-tunnel limit. For higher demands, you pair Cloud VPN with Cloud Interconnect or use the Dedicated Interconnect path for lower latency and higher aggregate bandwidth. Always verify current quotas and regional capabilities in the Console. Your mileage may vary based on routing, encryption, and the number of tunnels. Double-check the latest regional limits before planning a deployment.
What's the difference between cloud VPN and direct interconnect
Cloud VPN creates an encrypted tunnel over the public internet to a Google Cloud VPN gateway. It’s quick to deploy, inexpensive per tunnel, and flexible for site-to-site or remote worker access. Direct Interconnect provides a private, dedicated network connection into Google’s backbone with predictable low latency and much higher bandwidth. It’s worth it for steady, large-volume traffic or regulated workloads. If you’re optimizing cost and time-to-value, start with Cloud VPN. Scale with Interconnect as needs grow. Direct Interconnect is the sturdier backbone, Cloud VPN is the fast starter.
How do i secure a site-to-site VPN with cloud armor
Yes, you can add Cloud Armor to a Cloud VPN setup to harden the edge. Attach Cloud Armor policies to the VPN gateway’s external load balancer or the traffic path that enters your VPC. Start with a deny-all baseline and then carve allow rules for your known IPs and services. Use IP allowlists, rate limiting, and geo-blocking where applicable. Monitor logs in Cloud Logging to detect anomalies and adjust policies quickly. Cloud Armor rules should be kept tight. Overexposure invites risk.
Can i connect multiple on-prem sites to a single cloud VPN gateway
Yes. A single Cloud VPN gateway can be configured with multiple tunnels to different on-prem locations. Each tunnel maps to a distinct on-prem device or network segment, allowing a hub-and-spoke topology. Plan for redundancy by pairing primary and backup tunnels, and ensure you align BGP or static routes across sites. The architecture scales, but configuration gets intricate, document your route priorities and failover behavior. Multiple tunnels enable cost-effective, scalable connectivity.
Does Google cloud VPN work with third-party firewalls
Yes, you can insert third-party firewalls in the path. The VPN gateway handles IPsec, but you’ll often position a firewall in front of the VPC or at the on-prem side to enforce policy. Ensure the firewall supports the same IPsec/IKE proposals as Google Cloud VPN and mirror the tunnel endpoints precisely. Keep MTU, encapsulation, and NAT settings consistent across devices. Interoperability hinges on matching crypto and routing configs.
How is IPsec configured on Google cloud VPN
IPsec configuration on Cloud VPN uses IKEv1 or IKEv2 with predefined shared keys or certificates, depending on your on-prem device. You’ll specify the peer IP, the local and remote networks, the IKE version, the encryption and hashing algorithms, and the traffic selectors. Create one tunnel per peer, then enable BGP for dynamic routing if supported. Finally, test the tunnel bring-up and monitor the crypto statistics to confirm the SA lifetimes are healthy. Exact crypto settings must mirror the on-prem device.
What monitoring options exist for cloud VPN connections
Yes, you have several monitoring streams. Cloud Console provides tunnel status, uptime, and bytes transferred. Cloud Monitoring and Cloud Logging deliver per-tunnel metrics, health checks, and alerting. You can script probes to verify reachability, and export logs to SIEMs. For a fast pulse, watch the tunnel state and the number of active SAs. Align alerts with your SLA for downtime and degradation. Monitoring visibility is critical for proactive remediation.