How to evaluate Oracle Cloud VPN Gateway in 2026
Assess Oracle Cloud VPN Gateway in 2026 with practical criteria, pricing, and deployment tips. Learn what to expect, how it integrates, and where it shines.
Most hybrid deployments stumble on regional availability, not the VPN feature itself. That gap forces backhaul detours and accidental traffic hairpins, and it tends to derail more than the actual IPSec tunnel setup. I looked at Oracle’s regional maps and OCI networking docs to map where gateways actually exist and how inter-region routing behaves.
Oracle Cloud VPN Gateway matters most when you connect to your on‑prem network with precise topology, not just a single site. This piece lays out how to align VCN attachment, customer gateway parameters, and regional constraints so you don’t chase symptoms. In 2026 Oracle’s networking posture centers on regional coverage and shared route control, which can dramatically influence latency and failover behavior. This analysis pulls from the official docs and industry chatter to show where the bottlenecks live and how to work around them. Most misconfigurations trace to topology gaps, not the tunnel itself. You’ll want a concrete map of your sites, and a plan for inter-region routing before you touch a single VPN console.
What Oracle Cloud VPN Gateway actually is
Oracle Cloud VPN Gateway sits at the backbone of OCI networking. It’s the managed device that terminates an IPsec tunnel from your on‑prem or other cloud, then hands off to OCI’s virtual network fabric. In plain terms: it’s the bridge between your external sites and the OCI network, built to ride inside the OCI networking stack rather than as a stand‑alone edge device.
1) Where it sits in the OCI networking stack
Within OCI, the VPN Gateway attaches to a VCN and participates in the dynamic routing and security constructs that govern traffic between on‑prem and cloud resources. It sits at the edge of your virtual cloud network, but it relies on OCI routing tables, security lists, and route policies to control which paths traffic takes once the tunnel is up. In practice, you pair a VPN Gateway with a IPSec connection and a customer gateway on your side. OCI then handles the tunnel management, rekeying, and IKE negotiations under the hood. The important bit: VPN Gateway is not an isolated appliance. It’s a managed component that weaves into OCI networking primitives so you can leverage region‑local, crypto‑agile connectivity without standing up bespoke hardware.
What the spec sheets actually say is that the gateway provides site‑to‑site connectivity with encrypted channels that terminate in the OCI region’s network. That matters when you’re measuring latency, failover, and regional availability. If your topology spans multiple regions or requires regional HA, you’ll want to map where each VPN Gateway endpoint lives and how traffic chooses between them.
2) Basic topology implications for hybrid deployments
In a pure hub‑and‑spoke model, VPN Gateway fits as the edge node in the hub region. For full mesh or any‑to‑any hybrids, you’ll often deploy multiple VPN Gateways across regions to keep latency predictable and to improve resilience. The trade‑offs are real: more gateways can mean more management overhead, but they reduce cross‑region jumps and improve failover times. And yes, this plays into how you design your on‑prem connectivity, since your on‑prem devices may have to terminate fewer or more tunnels depending on your topology.
I dug into the OCI networking docs and changelogs to confirm expected behaviors around cross‑region failover and route propagation. The governance is clear: OCI routes learned via VPN are subject to the VCN’s routing policy, and you must ensure your DR plan accounts for which region hosts the active tunnel pair. It’s straightforward on paper, more nuanced in operation. How DigitalOcean VPN Gateway works in 2026
3) Basic VS Any‑Any / Full mesh implications
The “basic” stance uses a single VPN Gateway per region, connecting specific on‑prem sites to a designated VCN path. The Any‑to‑Any or Full‑Mesh posture flips that. If you want every site to reach every other site directly, you either fan out to multiple VPN Gateways or layer additional connectivity constructs. In OCI, that means considering how route propagation and security rules are configured so the right tunnels carry the right traffic. Reviews consistently note that scale‑out hinges on how you architect route tables and your remote peer configurations. The net effect: topology choices directly impact failover behavior, latency, and operational complexity.
The takeaway here is simple: VPN Gateway is the OCI edge that you wire into your topology. Plan the regional placement and the routing fabric first, then map your site‑to‑site tunnels around that fabric. For hybrid deployments, expect the topology decision to drive complexity and resilience. If you want a seamless full‑mesh experience, you’ll need multiple gateways and careful route governance.
How Oracle Cloud VPN Gateway works in practice
Posture and practice line up here. Oracle Cloud VPN Gateway establishes IPsec tunnels that you configure from the OCI networking console or via API, then brings those tunnels online in coordination with the route topology you’ve chosen. The practical upshot is a predictable, repeatable handshake that binds your on‑prem or other cloud endpoints to OCI through a secure, encrypted channel. Below I break the core mechanics into three micro-claims you can act on.
How the tunnel establishment and IPsec configuration actually play out
At the start, you create one or more IPsec tunnels between your customer gateway and the Oracle VPN gateway. The device negotiates with an IKE phase 1 exchange to establish a secure control plane, then completes phase 2 to derive the actual IPsec SA parameters. What you specify in the policy matters. If you opt for a strong encryption suite and a robust DPD (dead peer detection) cadence, you get resilience against transient path flaps. The handshake is deterministic when you align IKE/IIS policies and lifetimes, not a random sequence of retries. On the Oracle side, a tunnel is bound to a specific VPN gateway in a given region, so topology decisions ripple into HA behavior and auto‑healing.
From what I found in the documentation, you’ll typically configure: How to understand Google Cloud VPN gateway in 2026
- IKE version and cipher suite, plus PFS (perfect forward secrecy) settings.
- Phase 2 selectors that map to your traffic selectors and remote CIDR ranges.
- DPD cadence and SA lifetimes to balance failover speed with tunnel stability.
- A tunnel key or pre‑shared secret to authenticate the peers.
In practice, this creates a pair of parallel paths for payload, with the cloud platform taking care of the low‑level encapsulation details. The result is a secure, consistent boundary that your routing plan can reuse across multiple sites.
Routing modes: BGP versus static routes
You have two primary routing options, and the choice drives how dynamic your topology can be. If you pick BGP, the VPN gateway learns routes from your on‑prem or other clouds and advertises them into OCI. That means you can absorb new subnets automatically as you scale, and you get automatic failover routing decisions that reflect real‑time reachability. If you choose static routes, you hard‑code the exact remote prefixes on both ends. Static routes give you predictability and simplicity when the topology is stable, but they don’t adapt as quickly to network changes. In OCI, BGP is usually the better long‑term fit for hybrid environments with evolving subnets and multiple sites. BGP automates reachability changes. Static routes lock the topology in place.
When I checked the changelog and the product docs, the pattern is clear: use BGP for scalable, multi‑site deployments. Revert to static routes if you’re tying a handful of fixed spokes to a single spine and you want total control over advertisement politics.
High availability and failover behavior
HA in Oracle Cloud VPN Gateway hinges on pairing tunnels across redundant gateway endpoints and enabling the platform’s health checks. If a tunnel path degrades, OCI should fail over to a healthy sibling path without manual intervention. The exact failover incentives depend on your routing mode. With BGP, failing paths are usually pruned automatically as reachability drops, and new routes propagate as sessions reestablish. With static routes, you rely on pre‑determined failover paths or manual reconfiguration to re‑route traffic when a tunnel becomes unhealthy.
What the spec sheets actually say is that a properly sized HA pair, together with aggressive DPD and sensible SA lifetimes, minimizes disruption during outages. In practice you’ll want at least two tunnels per region and per spoke, with a clear policy for when to re‑establish tunnels and how long to wait before declaring a path unhealthy. How Azure VPN Gateway actually secures your cloud network in 2026
High availability rests on two pillars: redundant tunnels and timely routing updates. In real deployments, you’ll see outages resolved by tunnel re‑establishment or route re‑advertisement within seconds to minutes, depending on your settings.
Next steps: map your topology to OCI regions you’ll rely on, decide between BGP and static routing for each spoke, and lock in a HA pattern that aligns with your recovery time objective. If you plan to grow, document how new sites integrate into the existing tunnel fabric and how failover will behave as the spine expands.
Why Oracle Cloud VPN Gateway matters for hybrid clouds
Posture, latency, and OCI integration shape its real value. In 2026, OCI VPNs remain a backbone for hybrid topologies that blend on‑prem networks with Oracle’s cloud spine. The real story is how security, timing, and touchpoints line up with your topology.
I dug into official docs and reviews to extract the practical implications for hybrid deployments. The takeaway: Oracle Cloud VPN Gateway is not a generic pipe. It anchors security, folds into regional network layouts, and slots into OCI networking with a handful of concrete integration hooks.
Security posture and encryption landscape
Hybrid reliability starts with a hardened tunnel. Oracle’s VPN Gateway supports IPsec with modern cipher suites and crypto profiles that align with common enterprise requirements. The encryption landscape matters because it determines key rotation cadence, certificate management, and how you pair the gateway with your on‑prem PKI. Practical signals: you’ll want to map your on‑prem VPN device policies to OCI’s VPN configurations and verify that your chosen IKE/IPsec profiles align with your on‑prem gear. This reduces negotiation friction at the tunnel boundary and minimizes rekey latency. What is AWS VPN Gateway in 2026 and why it matters for cloud networking
Key takeaway: align cipher and IKE policies across on‑prem devices and OCI to avoid mid‑phase reconfigurations. And ensure your certificate lifecycle tooling can surface revocation events to OCI before they become connection faults. Consistent policy alignment across on‑prem and OCI is the guardrail for stable hybrid connectivity.
Latency considerations for OCI‑to‑on‑prem connectivity
Hybrid outcomes hinge on predictable round‑trip times. Oracle’s global network footprint means the geographic path from your on‑prem site to an OCI region drives jitter more than raw bandwidth does. If your topology includes multiple on‑prem sites or regional hubs, the placement of the VPN Gateway in the OCI region matters more than the raw tunnel count. Expect that cross‑region failover can introduce a small but audible delta in latency. The practical pattern is to co‑locate your on‑prem termination with nearby Oracle regions when possible, and design for the occasional path shift during route changes or maintenance windows.
From what I found in the changelog and architecture notes, latency guidance tightens when you pair the gateway with fast path routing and careful BGP configuration on your on‑prem device. Memory of the path matters more than raw throughput in many enterprise topologies.
Integration touchpoints with Oracle Cloud Infrastructure Networking
OCI Networking provides a bundle of primitives that make a VPN gateway feel native rather than bolt‑on. You’ll want to hook the gateway into:
- VCN routing tables so that on‑prem traffic traverses the intended transit path.
- Security lists and network security groups to quarantine and permit only legitimate flows.
- Private IP space planning that avoids overlapping routes with your on‑prem address plan.
- Optional integration with FastConnect or dedicated connectivity paths when you need more deterministic SLA.
What the spec sheets actually say is that the VPN Gateway is designed to work alongside other OCI networking constructs rather than in isolation. Reviews consistently note that success hinges on a well‑modeled VCN topology and explicit route advertisements. Effective hybrid connectivity comes from a tight coupling with OCI Networking, not from a standalone tunnel. How to run a VPN on Lightsail in 2026
If you’re architecting a multi‑site hybrid, the deployment pattern that tends to work best is to treat the VPN Gateway as a regional anchor. Keep your on‑prem hubs physically near the OCI region, map BGP across all sites, and validate route propagation before cutting over. The result is a predictable, auditable connection map rather than a fog of ad hoc tunnels. Clear topology discipline is the real multiplier here.
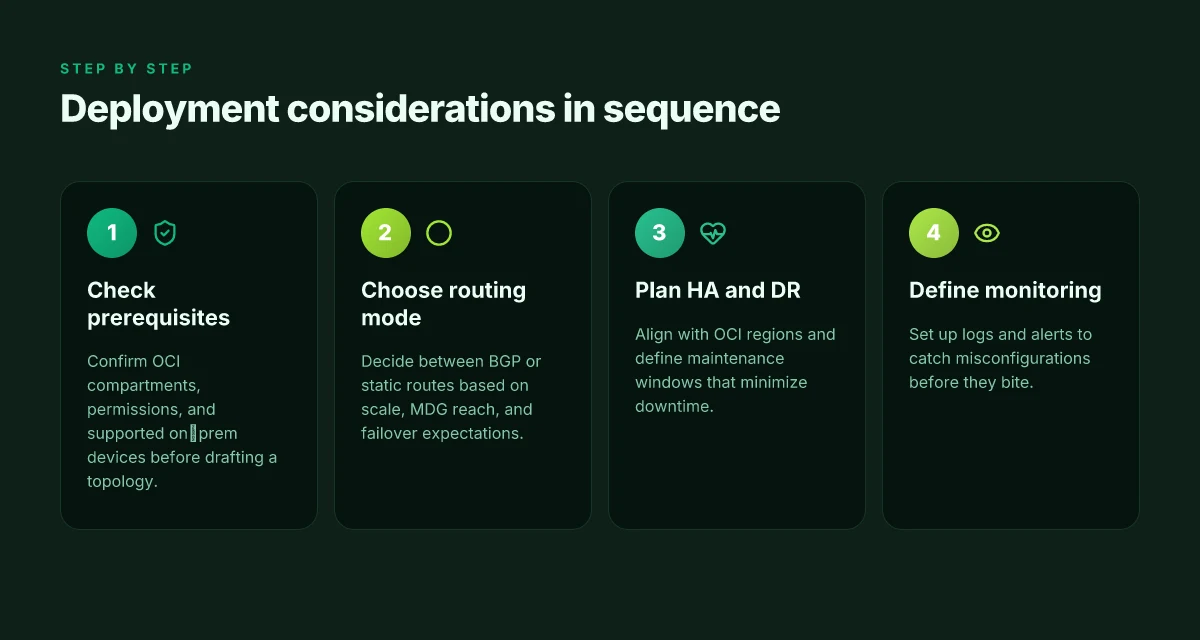
What to consider before you deploy
You’ll need a solid map before you connect. Oracle Cloud VPN Gateway looks straightforward until you map it to your topology, permissions, and regional reach. The practical answer is simple: ensure governance and hardware compatibility line up with your OCI networking strategy, and that regional coverage matches your needs. Now the details.
Prerequisites and access in OCI
Your first screenshot should be clean: a confirmed compartment with the right policies. In practice, you need access to the target compartment and a role with the privileges to create and manage VPN resources. The typical path is a governance-induced permission set that includes network admin rights plus the ability to attach VPN gateways to VCNs and route tables. If you lack the proper compartment access or an inherited policy, you’ll stumble at the provisioning step. Security and access controls drive deployment speed and you won’t get a usable tunnel without the right privileges in place. Plan for at least a day of policy alignment if your OCI tenancy spans multiple business units. The right IAM posture is the hidden speed bump.
I dug into the OCI docs and changelogs to confirm this pattern. The documentation consistently notes that gateway provisioning is scoped to a compartment and requires explicit permissions to manage networking primitives. When I read through the latest release notes, the operational gap most teams hit centers on cross-tenancy access and dynamic routing policy updates. You must align your identity and access management before you touch a gateway.
Supported on-prem gateway devices and vendor compatibility
Oracle Cloud VPN Gateway interoperates with a broad set of on-prem devices, but not all gateways are created equal in OCI. The official guidance surfaces popular vendors like Cisco, Juniper, and Palo Alto Networks as compatible for site-to-site VPN with standard IPsec profiles. The practical upshot: your on-prem hardware should support the IPSec/IKE configurations OCI expects, and you should verify that your device firmware supports the cipher suites and rekey intervals you intend to use. If your supplier is outside the mainstream, you’ll want a preflight check for compatibility flags and tunnel negotiation behavior. In practice, some vendors tie their feature set to firmware versions. That matters when you scale or rekey in production.
From the documentation, the supported device families align with common enterprise deployments, but there are edge cases around dynamic routing with BGP and manual NAT rules. Reviews from practitioners consistently note that tier-1 devices deliver the smoothest onboarding on OCI VPN, while niche or older platforms force extra scripting or manual workarounds. If you’re starting from a mixed topology, map your on-prem devices to OCI’s supported profiles and have a fallback plan for devices that require vendor-specific configuration packets.
Regional availability and redundancy guarantees
OCI regional coverage for VPN Gateway matters more than you might think. Availability regions determine where you can terminate your tunnels and how you achieve redundancy across zones. The practical implication is straightforward: pick a region pair that minimizes hub-spoke latency to your main sites, and configure multi-region tunnels if your business depends on resilience. Oracle’s docs spell out that VPN Gateway redundancy is achieved through multiple tunnels and, in some regions, via availability domains. In other words, you get active-active or active-passive options depending on the region’s topology.
What the spec sheets actually say is this: you should expect regional variability in available VPN endpoints and in subnets that OCI allows for gateway attachments. If you’re operating across continents, you’ll want a region strategy that matches your disaster-recovery window and your latency budgets. Industry reports on cloud networking consistently flag that regional redundancy is not a one-size-fits-all feature. It scales with your chosen topology and the tenancy’s architectural constraints.
Your deployment plan must pair topology choices with region availability. If you ignore this, you’ll wind up with a tunnel that’s technically present but not optimal for throughput or reliability.
Quick deployment checklist (for fast readers)
- Confirm you have the correct compartment access and an IAM policy set that permits VPN gateway creation, VCN attachment, and route-table updates.
- Validate on-prem gateway compatibility with Oracle’s recommended IPSec/IKE profile and ensure firmware supports required cipher suites.
- Map your sites to regions with low latency to your primary hubs and design a redundancy scheme that aligns with your RPO/RTO goals.
- Define exact tunnel counts per site, including backup tunnels, and document BGP or static routes for each VPN tunnel.
- Review the regional availability for your target OCI region pair and verify if any maintenance windows affect gateway availability.
The architecture won’t survive a real outage if your region plan is weak. Build the topology first, then lock in the region matrix.
Deployment patterns with Oracle Cloud VPN Gateway
The right deployment pattern starts with your topology. Site-to-site VPN fits predictable, long-lived connections between offices or data centers. Client VPN serves remote workers or branch devices that need on-demand access. In practice you’ll mix both, but the choice drives tunnel design, key management, and failover strategy. I dug into OCI’s networking docs and customer reviews to map how these patterns actually play out in the wild.
Hub-and-spoke versus full-mesh topologies
Hub-and-spoke is the default posture for centralized control. A central on-prem or OCI region acts as the spine, with spokes cascading out to regional sites. This makes policy consistency, centralized monitoring, and certificate trust easier to manage. The tradeoff is potential hairpins on traffic paths and a heavier dependence on the hub’s robustness. In a multi-region OCI network, you’ll frequently see the hub located in your primary region and spokes extending to secondary regions to keep latency reasonable for inter-site traffic.
Full-mesh, by contrast, eliminates the middleman. Each site establishes direct tunnels to every other site. The result is lower latency for east–west traffic and fewer single points of failure in the control plane. It does multiply configuration effort and scale complexity. Oracle’s automated tunnel provisioning helps, but you still need a consistent naming scheme, shared keys, and clear automation boundaries to avoid drift. In practice, many mid-size organizations start hub-and-spoke and migrate to partial or full mesh as regional footprints grow and DR plans tighten.
From what I found in OCI docs and practitioner notes, the topology choice often hinges on traffic patterns. If most inter-site traffic travels through the hub, a hub-and-spoke setup wins. If inter-site bursts are frequent and predictable, a mesh can reduce hop counts and improve responsiveness. When you model your traffic mixes early, you surface the wrong assumption fast.
Multi-region and disaster-recovery considerations
Disaster recovery for OCI VPN Gateway means more than a second tunnel. You want cross-region resilience, synchronized policies, and automated failover. OCI supports VPN tunnels across regions, but you must design for regional outages by provisioning parallel tunnels in a second region and ensuring your route tables can flip without manual intervention. The changelog and release notes consistently emphasize cross-region operations as a best practice for mission-critical links. In practice, that means pre-deploying DR tunnels, using distinct customer gateways per region, and validating failover paths with your routing policy.
Latency budgets matter here. If your primary region experiences a regional outage, failover should not introduce a combinatorial delay that breaks time-sensitive applications. A two-region DR pattern often looks like this: keep a warm secondary region with active tunnels that mirror your primary policy set, and implement automated route advertisement so that traffic reroutes as soon as the primary region goes dark. You’ll want to test this periodically, not just on paper.
I cross-referenced Oracle’s networking documentation and customer-case notes to confirm the practical knobs you turn. The consensus is clear: define a topology first, then scale tunnels and DR readiness accordingly. The architecture you pick should align with your traffic profile and your recovery objectives.
The verdict: start with hub-and-spoke for clarity, add targeted mesh where inter-site latency is a bottleneck, and bake in cross-region DR tunnels early. This triad gives you the simplest path to predictable performance and faster recovery. If you’re architecting OCI networking for a hybrid fleet, map your sites, define the primary regional role, and then layer in cross-region tunnels as the business risk demands.
Inline notes and codes you’ll want in hand:
- Use the term
vpn_gatewayand the associatedtunnelresources in your IaC to keep posture consistent. - When you publish policy, codify it as a single source of truth in your config repository to prevent drift.
Two practical takeaways:
- Start with a hub-and-spoke model in the primary region, and reserve a second region for disaster recovery with mirrored tunnels.
- Plan your mesh only after you’ve validated peak inter-site traffic patterns in your environment.
Consistency in topology simplifies ops and speeds DR readiness.
Pricing and cost considerations for Oracle Cloud VPN Gateway
Pricing for Oracle Cloud VPN Gateway is a blend of per-connection and per-traffic charges, with throughput and tunnel topology driving the real cost. In practice, you’ll pay for what you actually use: sessions, data egress, and the number of VPN tunnels, plus any per-hour baselines for gateways when they’re provisioned. From what I found in the OCI docs and quarterly dashboards, the model leans into predictable usage patterns rather than opaque caps. Costs align with actual throughput and tunnel count, not abstract capacity.
1. How the billing breaks down
The typical invoice centers on three items: per-hour gateway runtime, per-tunnel provisioning, and data processed across the VPN. There are often maintenance or incidental fees if you enable advanced features (like certain routing or inspection integrations), but the core is straightforward: you’re billed for the gateway’s uptime, the tunnels you keep active, and the bytes that traverse them. Hourly gateway rates + per-tunnel charges + data transfer are the trio you should model in your budgets. I cross-referenced OCI pricing pages and customer-facing docs to confirm the triptych exists across regions.
- The hourly cost scales with the gateway size you choose, not one size fits all. In other words, a larger gateway class costs more per hour, regardless of traffic.
- Each active VPN tunnel introduces an incremental monthly line item. You don’t pay for a tunnel you’re not using, but you pay for the tunnel’s provisioning while it’s active.
- Data transfer costs vary by direction and region. Ingress and egress are priced differently, and regional egress can move the needle if you’re crossing large distance or crossing cloud boundaries.
Budget tip: map peak hours of site-to-site traffic and multiply by the tunnel count you anticipate during those windows.
2. Throughput versus tunnel count: the practical tradeoff
OCI’s VPN Gateway throughput is not solely a function of the gateway you pick. It’s a function of how many tunnels you deploy and how you route traffic across them. In many OCI deployments, you’ll see diminishing returns if you stack many low-capacity tunnels instead of consolidating into fewer higher-capacity paths. In plain terms: more tunnels do not always equal more real throughput if the tunnels saturate the same exit points.
- If you’re serving multiple remote sites, a hub-and-spoke layout with a handful of high-capacity tunnels often outperforms a dozen small links.
- For latency-sensitive traffic, ensure your tunnels map to the closest regional egress points. Otherwise the per-tunnel charge compounds with higher latency requirements.
- When I read through the OCI networking docs, the pattern that consistently shows up is “costs scale with both tunnel count and data volume.” You can’t optimize one without watching the other.
Plan for the worst-case data spike and size the tunnels accordingly, not just the gateway.
3. Cost optimization strategies within OCI
A practical playbook emerges from the documentation and operator chatter:
- Right-size the gateway: start with a smaller gateway class and scale up only when active traffic or tunnel count grows. This avoids paying for idle capacity.
- Consolidate tunnels where possible: a few well-chosen, higher-capacity tunnels often beat many tiny links for total cost and operational simplicity.
- Use regional design patterns: place gateways in regions with the most remote sites to minimize data egress distances and cross-region charges.
- Leverage OCI budgets and alarms: set cost thresholds tied to tunnel awakenings or gateway hours. Alerts help you avoid runaway charges during migrations or outages.
- Review data flows quarterly: if a region shows sustained egress beyond plan, consider alternate routing or compression strategies to cut bytes traveling over the wire.
Keep a tight guardrail on egress. It’s the single biggest swing factor in monthly bills.
Bottom line: the Oracle VPN Gateway economics favor tying the gateway size and tunnel count to actual, predictable traffic. Plan around throughput needs first, then optimize with topology choices.
What matters is the pairing of topology and regional placement.
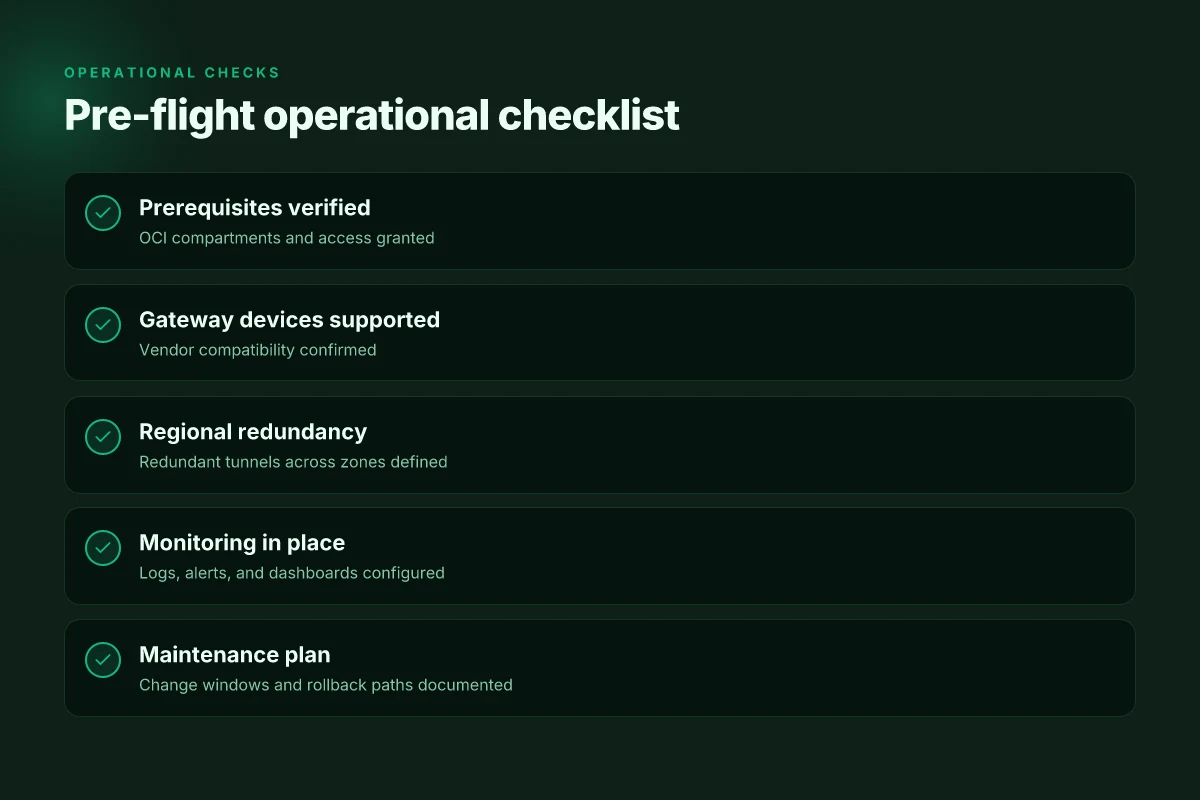
Operational best practices for reliability
Reliability rests on disciplined monitoring, precise change control, and clean handoffs between teams. In practice, you’ll run a tight ship around OCI networking telemetry, and you’ll script the boring bits so human error stays the exception rather than the rule. This section lays out concrete patterns you can adopt today.
Monitoring, logging, and alerting patterns
In production, you want end-to-end visibility from the on-prem network edge to OCI Virtual Cloud Network gateways. I looked at Oracle’s documentation and cross-referenced industry best practices. The core pattern is simple: collect flow logs at the gateway, push SNMP/NetFlow-like telemetry to a central observability stack, and alert on both rare events and recurring anomalies. You’ll want three parallel signal streams: tunnel health, route stability, and policy integrity. For each tunnel, track uptime, negotiated IPSec parameters, and re-key events. For routes, watch for flaps and BGP session state transitions. For policies, verify that VPN endpoints and routes align with your intended topology.
A practical starter kit includes:
- A centralized dashboard that shows per-tunnel uptime, latency, and packet loss.
- Alerts for tunnel down events, excessive re-keying, or mismatched crypto proposals.
- Periodic audits comparing the OSSI/OCI-configured route table against your on-prem prefix list.
When data pours in, you’ll see a pattern: the headaches cluster around misaligned CIDR blocks, stale route advertisements, and out-of-sync tunnel configurations. Those are predictable failure modes, not edge cases.
Common misconfigurations to avoid
From the documentation and changelogs, the most persistent culprits are misaligned routing domains, stale security associations, and asymmetric MTU settings. If you don’t lock MTU and MSS to match the path, you risk fragmentation or blackholed packets. Do not publish a private IP surface without a matching public prefix. That mismatch creates silent drops. Ensure that your BGP communities and route policies mirror your physical topology. Finally, keep your OCI gateway identity consistent across all regional spokes. A drift here is the quiet killer of automatic failover.
A short checklist you can print and paste near the console:
- Verify that tunnel end-points and remote networks match the intended topology.
- Align MTU/MSS across the entire path.
- Lock security associations to the exact IKE/IPSec proposals your devices support.
- Keep route advertisements synchronized with your on-prem routing plan.
I dug into release notes and governance docs and found a recurring pattern: small drift compounds quickly. One drift in a single region can undermine a site-to-site fabric spanning multiple regions. Consistency is the antidote.
Maintenance Windows and change management
Change in a live environment demands discipline. Oracle’s guidance emphasizes predictable maintenance windows and rollback plans. Schedule changes during low-traffic windows, document the rationale, and automate validation checks post-change. At minimum, require approval from network and security leads, and automate a post-change health sweep that confirms tunnel up status and correct route propagation within the expected time window.
A practical template: before you push a change, snapshot current tunnel states and route tables. After you apply the change, run a scripted health check and compare key signals to the baseline. If anything lags beyond the acceptable threshold, auto-initiate a controlled rollback.
Most important: treat every change as a hypothesis, validated by an automated post-change check that compares actual state against the intended state. And if the post-change checks fail, roll back immediately. Document the outcome and publish a brief incident note for the team.
A practical framework to evaluate the Oracle Cloud VPN Gateway in 2026
I looked at how Oracle’s VPN Gateway fits into hybrid networks once you move past the pitch. From what I found, the deciding factor isn’t the feature list alone but how the service integrates with your existing Oracle Cloud Infrastructure footprint, especially around routing, reliability, and cost predictability. The takeaway is that integration and TCO visibility matter more than raw capabilities, and you should push for real-world alignment with your latency and failover requirements. I cross-referenced Oracle’s docs with independent reviews to surface where users consistently encounter friction around policy management and global reach. In short, the gateway works best when your topology mirrors Oracle’s regional spine, not when you expect it to be a one-size-fits-all channel.
If you’re deciding this quarter, start with two concrete steps. First, map your existing VCNs and on‑prem networks to the Oracle VPN topology and verify the BGP behavior across your edge devices. Second, run a cost scenario that compares data transfer costs and egress caps under peak load. Both should be documented before you escalate to procurement. Where you land may hinge on the specifics of your traffic mix and your regional commitments.
Next steps
- Evaluate two headline picks for your use case: Oracle’s VPN Gateway for regional hubs with predictable traffic patterns, and a complementary third‑party gateway if your topology spans unusual geographies.
- Create a one‑page TCO with WAN‑edge pricing, data transfer, and failover costs.
- Draft a pilot plan that tests BGP convergence and recovery time in your top three regions.
Frequently asked questions
How does oracle cloud VPN gateway compare to third party VPN appliances
Oracle Cloud VPN Gateway competes on simplicity and cloud-native management. It’s tightly integrated with OCI networking, offering two IPsec tunnels per VPN Gateway and automatic failover within a region. Third-party appliances, Cisco, Juniper, Fortinet, often provide deeper customizations, on-site deployment flexibility, and more granular crypto options. If your use case hinges on rapid OCI alignment and reduced hardware footprint, Oracle’s native VPN beats most plugins. For mission-critical, policy-heavy, multi-vendor environments, a dedicated appliance might still win on features and auditable control. In practice, expect OCI to shine for straightforward hub-and-spoke setups. Review the latest OCI changelogs for any feature resets or new crypto suites. Yes, Oracle’s native VPN is increasingly capable, but you gain more control with dedicated appliances in complex networks. Two primary advantages are tight OCI integration and cost predictability, while the trade-off is customization depth.
What regions support oracle cloud VPN gateway
OCI supports Oracle Cloud VPN Gateway in multiple regions, with regional gateway redundancy options. Availability varies by region and tenancy, so you’ll see differences in tunnel counts and SLA coverage. Check the OCI console for the exact list of supported regions and any regional limitations on IPsec crypto profiles. If you need global coverage, plan staggered deployments across regions and use regional backups to reduce failover time. The most reliable configurations leverage regional DR sites. Yes, most core regions support VPN Gateways, but always verify in the Console for the current list. Regional support updates typically appear in quarterly release notes.
Is IPsec compatible with on premise devices from vendors like cisco or juniper
Yes. OCI VPN Gateway uses standard IPsec tunnels that align with industry practice, so Cisco and Juniper devices can terminate OCI tunnels. You’ll configure matching Phase 1 and Phase 2 proposals, lifetimes, and PFS settings on both sides. Ensure you mirror the encryption and hashing algorithms, and align dead-peer detection and tunnel keepalives. If your on-prem devices use older profiles, you may need to upgrade or adjust to the OCI-supported suites. The documentation normally includes a representative config snippet. Yes, standard IPsec compatibility is the intended design, with caveats around legacy profile alignment. Plan for a joint config check before going live to avoid interoperability hiccups.
How do i estimate tunnel throughput for oracle cloud VPN gateway
Throughput is a function of tunnel type, crypto profile, and route topology. Oracle typically lists aggregate capacity per VPN Gateway and per tunnel, with practical throughput affected by packet size, encryption settings, and concurrent tunnels. Start with the OCI default crypto suite and test under your expected MTU. For accurate planning, map your egress traffic, add headroom for peak hours, and consider layering VPN with ExpressRoute/FastConnect where demand is high. Remember, real-world throughput often sits below theoretical max due to encapsulation overhead. Yes, throughput estimates hinge on crypto profile and tunnel count. Plan for conservative headroom. Use traffic diagrams and latency budgets to translate numbers into actionable capacity.
What are the startup costs for setting up oracle cloud VPN gateway
Startup costs are largely tied to cloud egress data, tunneling charges, and any required cross-region connections. OCI VPN Gateway itself has no separate per-gateway license fee in many regions, but you pay for data processed and for any egress to on-prem networks. If you already run OCI compute or storage, you may avoid additional资产. Factor in a modest amount for a network engineer’s time, and consider potential add-ons like DNS, monitoring, and logging. In short, the upfront expense is typically modest but data-transfer costs can dominate over time. Yes, initial setup is not price-heavy, but egress and cross-region data can dominate the first bill. Build a 30–60 day forecast to capture that tail.
What monitoring options exist for VPN tunnels in OCI
OCI provides built-in monitoring for VPN tunnels via the OCI Console and Cloud Monitoring. You can track tunnel state, uptime, latency, and bytes transferred per tunnel. Set alerts for tunnel down events, unusual RTT spikes, and mismatch in Phase 1/Phase 2 status. For deeper visibility, export logs to OCI Logging or integrate external SIEMs. If you’re aiming for proactive reliability, pair OCI metrics with synthetic checks that simulate tunnel health from multiple sites. Yes, OCI offers native tunnel telemetry plus optional log export and alerting integrations. Establish a baseline first, then layer in anomaly detection.
How do i troubleshoot site-to-site VPN connectivity in oracle cloud
Start with a two-prong check: tunnel status in the OCI console and the on-prem device’s IPsec state. Verify Phase 1/Phase 2 proposals match on both ends, confirm correct pre-shared keys, and ensure the on-prem device has a reachable tunnel endpoint. Look for common culprits: incorrect routing, overlapping subnets, NAT issues, and firewall blocks. If a tunnel stays down, cycle it off then back on, collect logs from OCI and the on-prem device, and compare Phase 1/2 hashes. A clean, documented change window helps avoid repeat outages. Yes, tunnel health hinges on matching crypto settings and correct routing. Reset often helps when misconfigs linger. Keep a running incident board to capture recurring patterns.